USB Rubber Ducky Keystroke Injection Tool for Covert Exploits With Reverse Shell images
USB Rubber Ducky Keystroke Injection Tool for Covert Exploits With Reverse Shell
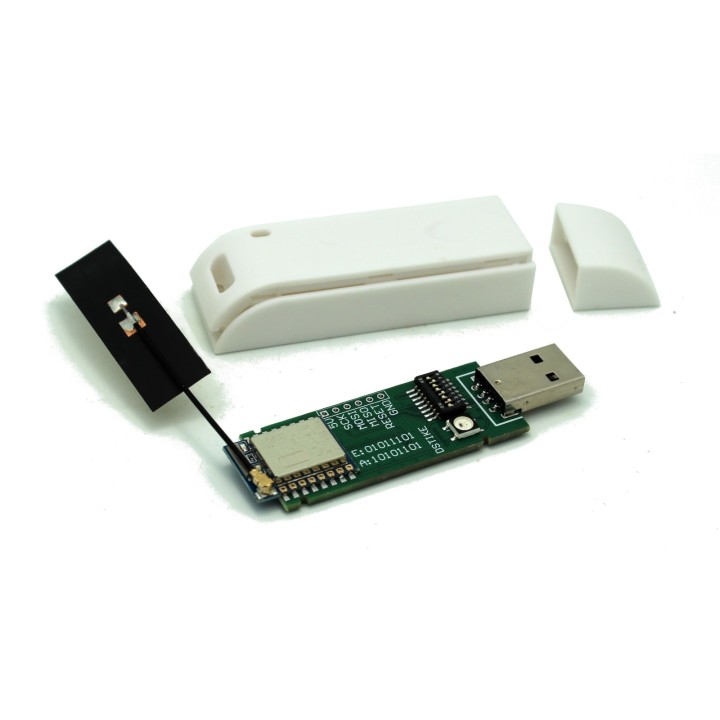
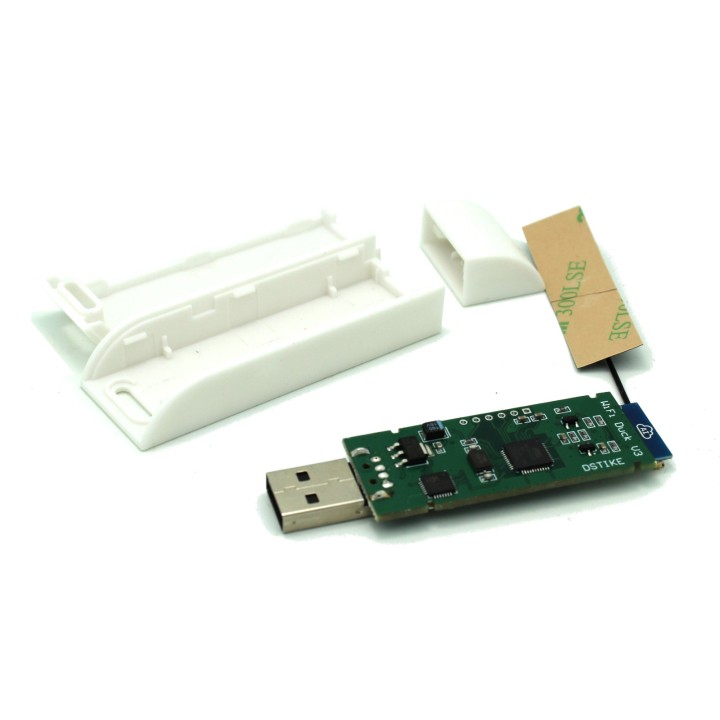
This device allows keystrokes to be sent via WiFi to a target machine. The target recognises the Ducky as both a standard HID keyboard and a serial port, allows interactive commands and scripts to be executed on the target remotely.
This device allows keystrokes to be sent via WiFi to a target machine. The target recognises the Ducky as both a standard HID keyboard and a serial port, allows interactive commands and scripts to be executed on the target remotely.
WIKI Page: https://github.com/whid-injector/WHID/wiki
Third-Party Software Compatible with WHID’s Hardware
- https://github.com/whid-injector/WHID/tree/master/ESPloitV2_whid (Improved version of WHID GUI, installed by default on Cactus WHID hardware)
- https://github.com/sensepost/USaBUSe (Dedicated software for AirGap bypass Vs Windows)
- https://github.com/spacehuhn/wifi_ducky (old software similar to ESPloitV2)
- https://github.com/basic4/WiDucky
HOW TO START
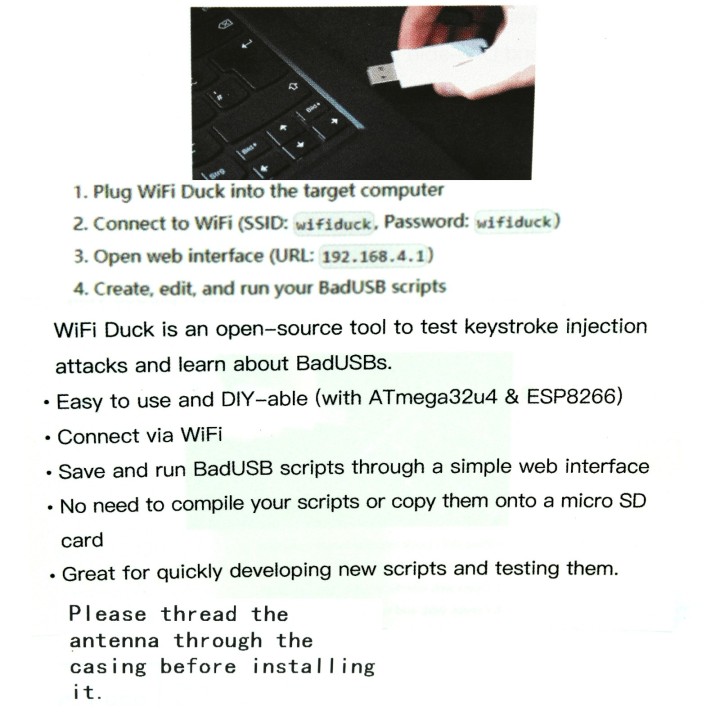
Just plug it in a USB port and connect to the WiFi network: SSID "Exploit"
Password "DotAgency"
Open a web browser pointed to "http://192.168.1.1"
The default administration username is "admin" and password "hacktheplanet".
https://github.com/exploitagency/ESPloitV2
For cool payloads or more info check the Wiki or the Payloads directory.
-
Brand

-
ReferenceTS3090
4 other products in the same category
Clients also bought